Togo Law 2019-014 and AI: What the IPDCP Expects from Companies
The IPDCP has been active since March 2025. What Togo's Law 2019-014 requires from companies that use ChatGPT, Copilot or Gemini with personal data.
In just a few years, Togo has built a serious reputation in cybersecurity. A dedicated law since 2018, a national agency, an incident response center. Since March 2025, the country also has a working data protection authority: the IPDCP.
For companies in Lomé and beyond, this changes things. Law No. 2019-014 is no longer a text waiting for its regulator. And the question of artificial intelligence is now very concrete: what can be sent to ChatGPT, Copilot or Gemini without breaking the law?
Law No. 2019-014 at a glance
Law No. 2019-014 of 29 October 2019 on the protection of personal data sets the basic rules. It does not mention AI, but it applies as soon as information can identify a person.
Prior declaration. Processing must be declared in advance to the IPDCP, which issues a receipt within one month at most.
Authorization for sensitive data. Genetic, health and biometric data, as well as data on offences, require prior authorization.
Classic principles. A defined purpose, relevance, limited retention, accuracy and transparency.
Security. The data controller must ensure the confidentiality and security of the data.
Individual rights. Information, access, objection, rectification and erasure.
The IPDCP: an authority now up and running
The Personal Data Protection Authority (IPDCP, Instance de protection des données à caractère personnel), an independent administrative authority created by the 2019 law, officially launched its activities on 28 March 2025 in Lomé. Its first priority is raising awareness among the media, public administrations, businesses and the general public. Sanctions will come later.
Its action plan includes a digital academy, a network of focal points, sector barometers, maturity indicators and certification for the most advanced organizations. In other words, the IPDCP is going to measure who is compliant.
For companies, this planned certification is also an opportunity. In public tenders and with foreign partners alike, being able to show that you control your data is becoming a commercial argument. It is better to prepare early, especially since generative AI multiplies data flows that are hard to track.
The law gives it real powers: document and on-site inspections, temporary then permanent withdrawal of an authorization, and administrative fines of up to 100 million CFA francs. Some offences, such as failing to complete prior formalities, also carry criminal penalties.
A country that bet on cybersecurity
The data protection framework is part of a broader set:
Law No. 2018-026 on cybersecurity and the fight against cybercrime;
the National Cybersecurity Agency (ANCy), created in 2019, which defines and applies national policy;
CERT.tg, the national incident response center;
Cyber Defense Africa, a joint venture set up in 2019 with the Polish group Asseco Data Systems.
Togo is also no stranger to large-scale data use. During the Covid-19 pandemic, the Novissi cash transfer program used mobile phone data and satellite imagery to target households. The data culture is there. The culture of protecting that data needs to keep pace.
What the law changes for AI use
Every AI use with personal data is processing
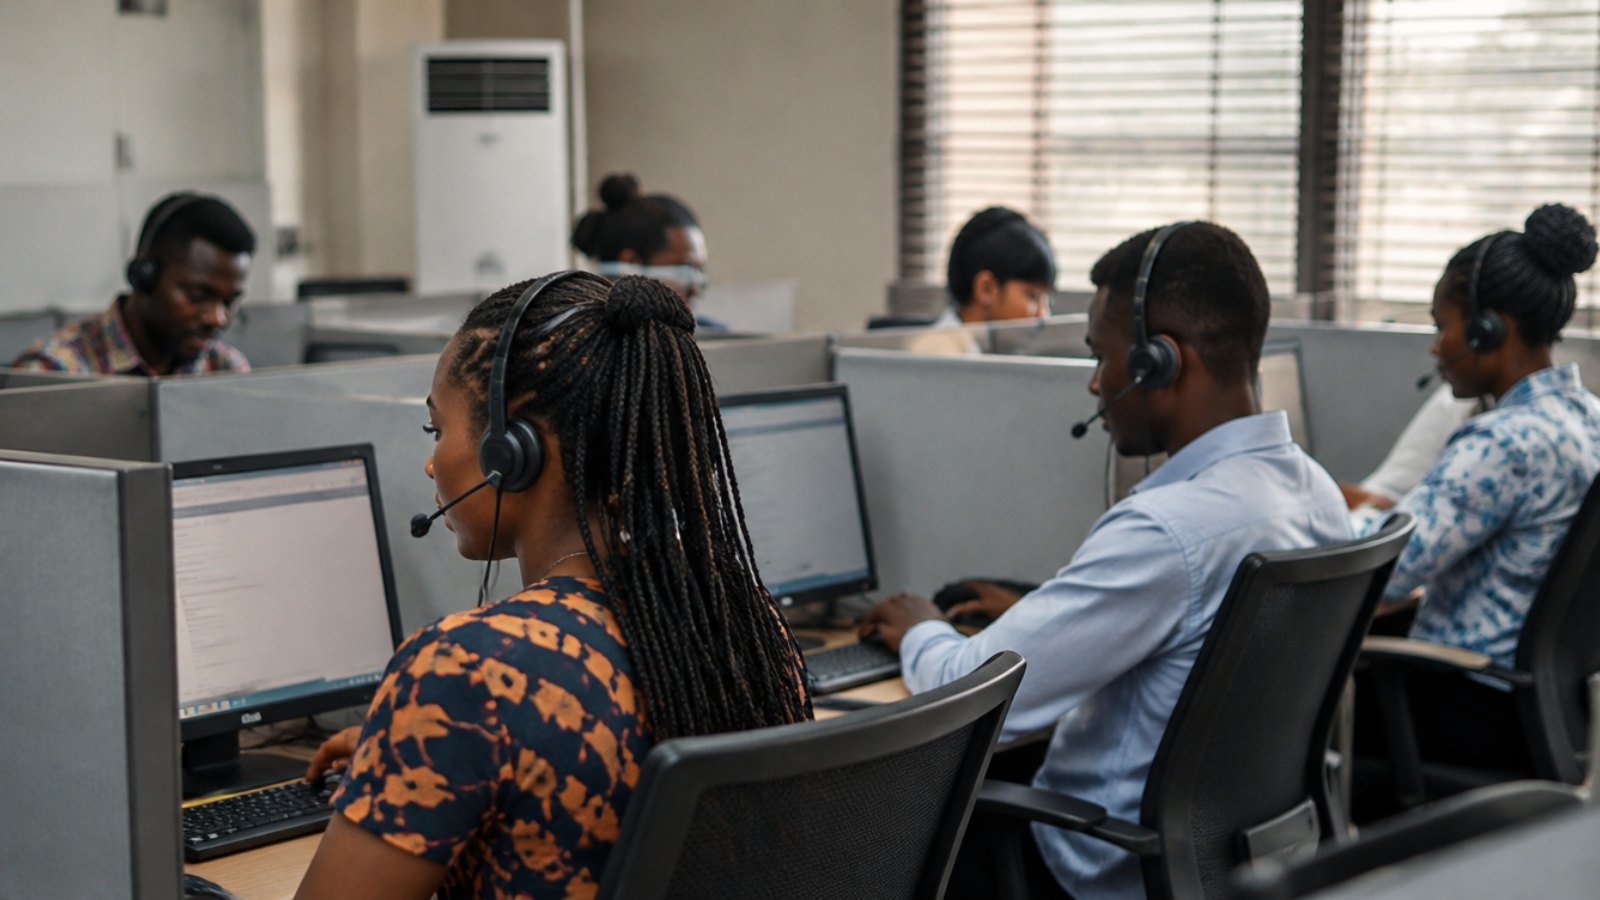
When a call center agent pastes a subscriber's history into a chatbot, that is processing. It must have a clear purpose and fall within the scope declared to the IPDCP.
Sensitive data calls for maximum caution
A medical report, biometric data or a criminal record should never go to a consumer AI assistant. Processing them requires authorization, and simply sending them out can be a problem.
Security is not delegated to the AI vendor
The company remains the data controller. If an employee exposes data through an external tool, the company will have to answer for it. We walk through this scenario in the anatomy of an AI data leak.
AI agents widen the attack surface
Assistants connected to email, customer databases or internal tools can be hijacked by hidden instructions. See our analysis of prompt injection attack patterns.
Getting ready before the first inspections
Five steps are enough to deal with most of the risk:
List the AI tools in use and the data that flows through them.
Update your declarations to the IPDCP to cover these uses.
Prohibit sending sensitive data to external tools, and enforce it technically.
Automatically anonymize personal data before anything is sent.
Keep a log of prevented incidents, useful during an inspection or a certification process.
To see Togo in its regional context, read our article on generative AI and data protection in West Africa.
Where ZeusLock fits
ZeusLock works on employees' devices and browsers. It detects personal and sensitive data in real time in prompts and files sent to AI assistants, then anonymizes it while keeping its format, warns the user or blocks the request, depending on your rules. Every event is logged, so you have concrete evidence to show the IPDCP.
Key takeaways
With a 2019 law, an authority active since 2025 and a structured cyber ecosystem, Togo is entering an enforcement phase. The IPDCP is starting with education, but it will soon measure how mature organizations are. Companies that govern their AI use now will be in a strong position.
Want to measure your teams' exposure? Request a ZeusLock demo.
Protect your data from AI leaks
See ZeusLock stop sensitive data before it reaches ChatGPT, Claude, Gemini and more, in a 30-minute demo.