Madagascar Law 2014-038 and AI: protecting client data in offshoring
Call centers and BPOs in Antananarivo handle French client data with AI tools. What Law 2014-038, the CMIL and the GDPR require, and how to act on it today.
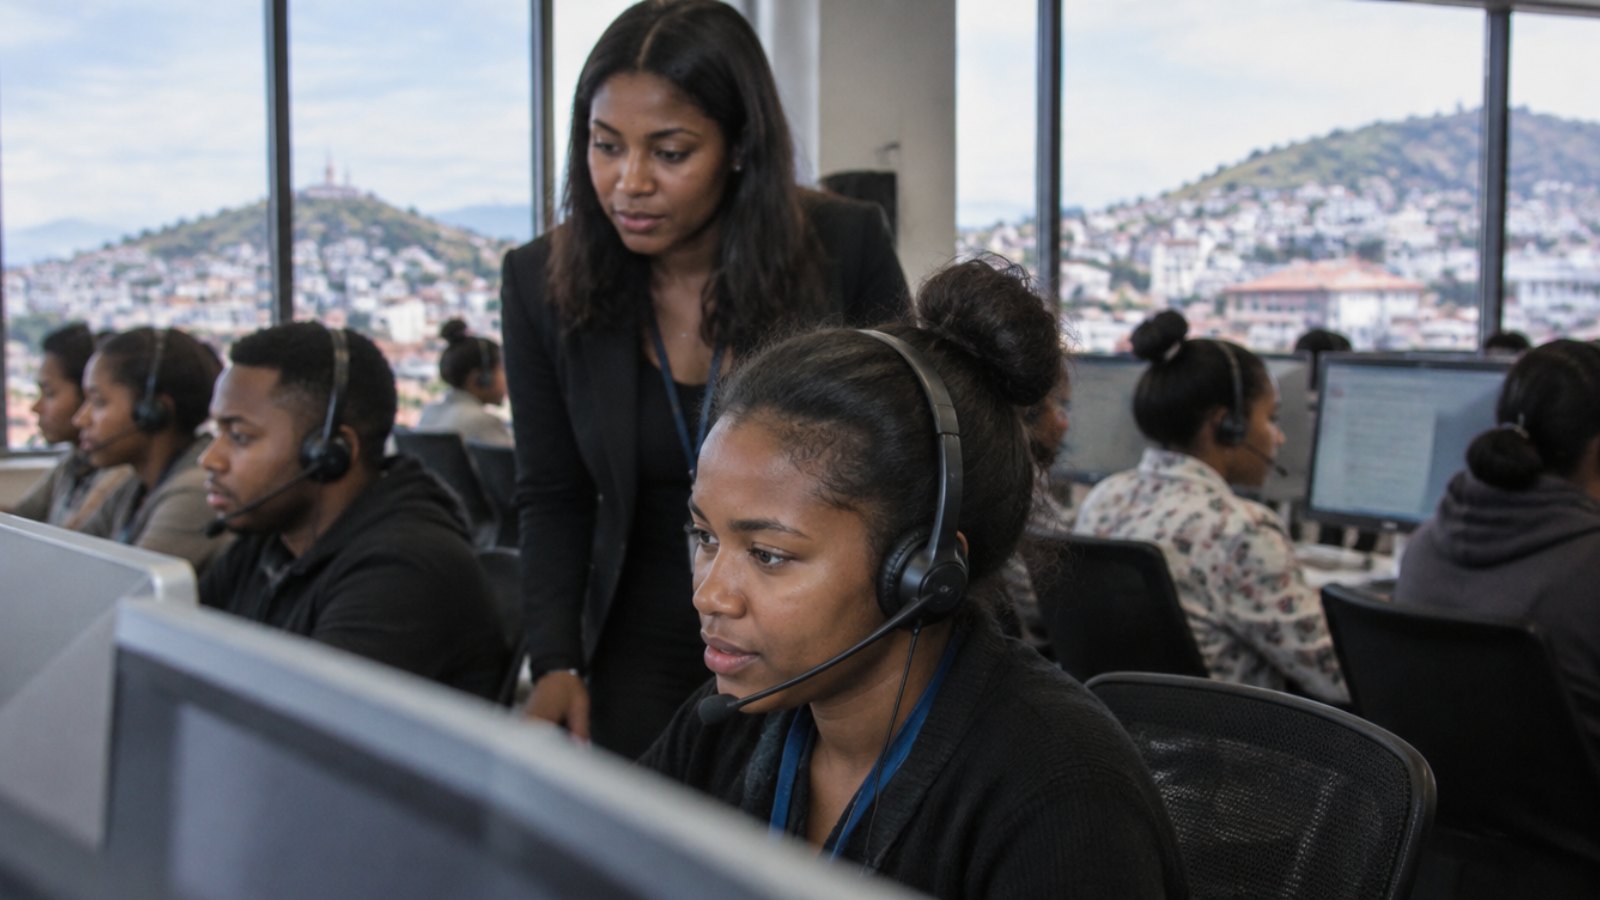
In Antananarivo, an agent answers a subscriber of a French telecom operator while her colleague processes insurance claims for a European insurer. Between calls, many of them open ChatGPT or Copilot to rephrase a reply, summarize a conversation or translate a letter. It saves time. It is also the moment when data that does not belong to them leaves the workstation.
For Malagasy outsourcing companies, this is a very practical question. They are bound by Madagascar's Law No. 2014-038 on the protection of personal data, and their European clients remain bound by the GDPR. Now that generative AI has reached the call center floor, the two frameworks meet in every single prompt.
An industry built on its clients' data
Outsourcing has become one of the main drivers of urban employment in Madagascar. According to International Finance Corporation figures reported by L'Express de Madagascar in 2025, the sector accounts for about 45,000 jobs and could reach 100,000 by 2030. More than 230 companies operate in it, and over 80% of their clients are French businesses.
The model runs on trust. A client hands a provider in Tana its customer files, complaint histories and sometimes banking or health data. The same article notes that tools such as ChatGPT, Microsoft Copilot and internal chatbots are already used in the sector. In most cases, this use is neither disclosed to the client nor covered by the contract.
What Law 2014-038 says
Law No. 2014-038 follows principles that will look familiar to anyone who knows European data protection. It applies to processing carried out in Madagascar, including on behalf of foreign companies. Its core rules include:
purpose limitation: data may only be used for the purpose it was collected for;
proportionality: only the data that is actually needed should be processed;
security: the controller and its processor must protect data against unauthorized access and disclosure;
controls on transfers to countries that do not offer an adequate level of protection.
Pasting a customer record into an AI assistant hosted abroad is at once a new use of the data, a disclosure to a third party and, very often, a transfer out of the country.
The CMIL is finally stepping out of the shadows
The law creates a supervisory authority, the Malagasy Commission on Informatics and Liberties (CMIL). For years it existed only on paper. As late as February 2025, the Malagasy press lamented that the commission had still not been set up, during an assessment mission supported by the Francophonie.
That has changed. In February 2026, the CMIL announced it had entered a phase of stronger operational activity: structuring its governing bodies, training its members with an expert from the OIF, and registering several dozen files, mostly compliance requests. The law gives it the power to issue warnings, impose administrative fines and order the seizure of a database.
The GDPR travels with the files
Madagascar does not have an adequacy decision from the European Commission. French clients therefore rely on standard contractual clauses and a processing agreement under Article 28 of the GDPR. That agreement lists the approved sub-processors and the expected security measures.
An agent who uses a consumer AI assistant is quietly adding a sub-processor that nobody approved. After an incident or during an audit, the Malagasy provider will have to explain what left, to which service and why. Our EU AI Act and GDPR compliance checklist covers the evidence European clients increasingly ask for.
Where the risk shows up on the floor
Leaks rarely come from bad intent. They come from everyday habits meant to save time:
pasting a full customer conversation, with name, address and contract number, to get a more polished reply;
asking for a summary of a claim file or a bank statement;
translating a complaint letter that contains an IBAN or medical details;
uploading a ticket export to pull statistics from it.
Banning AI does not work: agents simply switch to their phones, outside any control. We describe this pattern and what it costs in the real cost of shadow AI.
Keep the AI, remove the data
The sensible approach is to let agents use AI while controlling what goes into their prompts. In practice, a provider can:
map the AI tools actually used on each floor;
update contracts and the sub-processor list with every client;
detect sensitive data automatically before it is sent, then anonymize it, warn the agent or block it;
keep an incident log to answer client audits and CMIL requests.
Format preserving anonymization helps a lot here: a name becomes another name, a contract number keeps its structure, and the assistant can still produce a usable answer. For a wider view of the continent, see our analysis of AI and data protection in West Africa.
Key takeaways
Madagascar's BPOs and call centers mainly process data belonging to European clients. Law 2014-038 governs that processing, the CMIL is becoming operational, and the GDPR applies through contracts. Generative AI is already on the floor. The real question is no longer whether it is used, but whether you can prove it is used without exposing data.
ZeusLock detects, anonymizes or blocks sensitive data before it reaches ChatGPT, Copilot or Gemini, directly on the agent's device, and keeps a record of every incident. Book a demo to see how it fits your operations.
Protect your data from AI leaks
See ZeusLock stop sensitive data before it reaches ChatGPT, Claude, Gemini and more, in a 30-minute demo.