Tunisian banks and insurers: managing generative AI in practice
Law 2004-63, banking Law 2016-48, BCT Circular 2021-05: how Tunisian banks and insurers can manage generative AI and protect customer data in daily work.
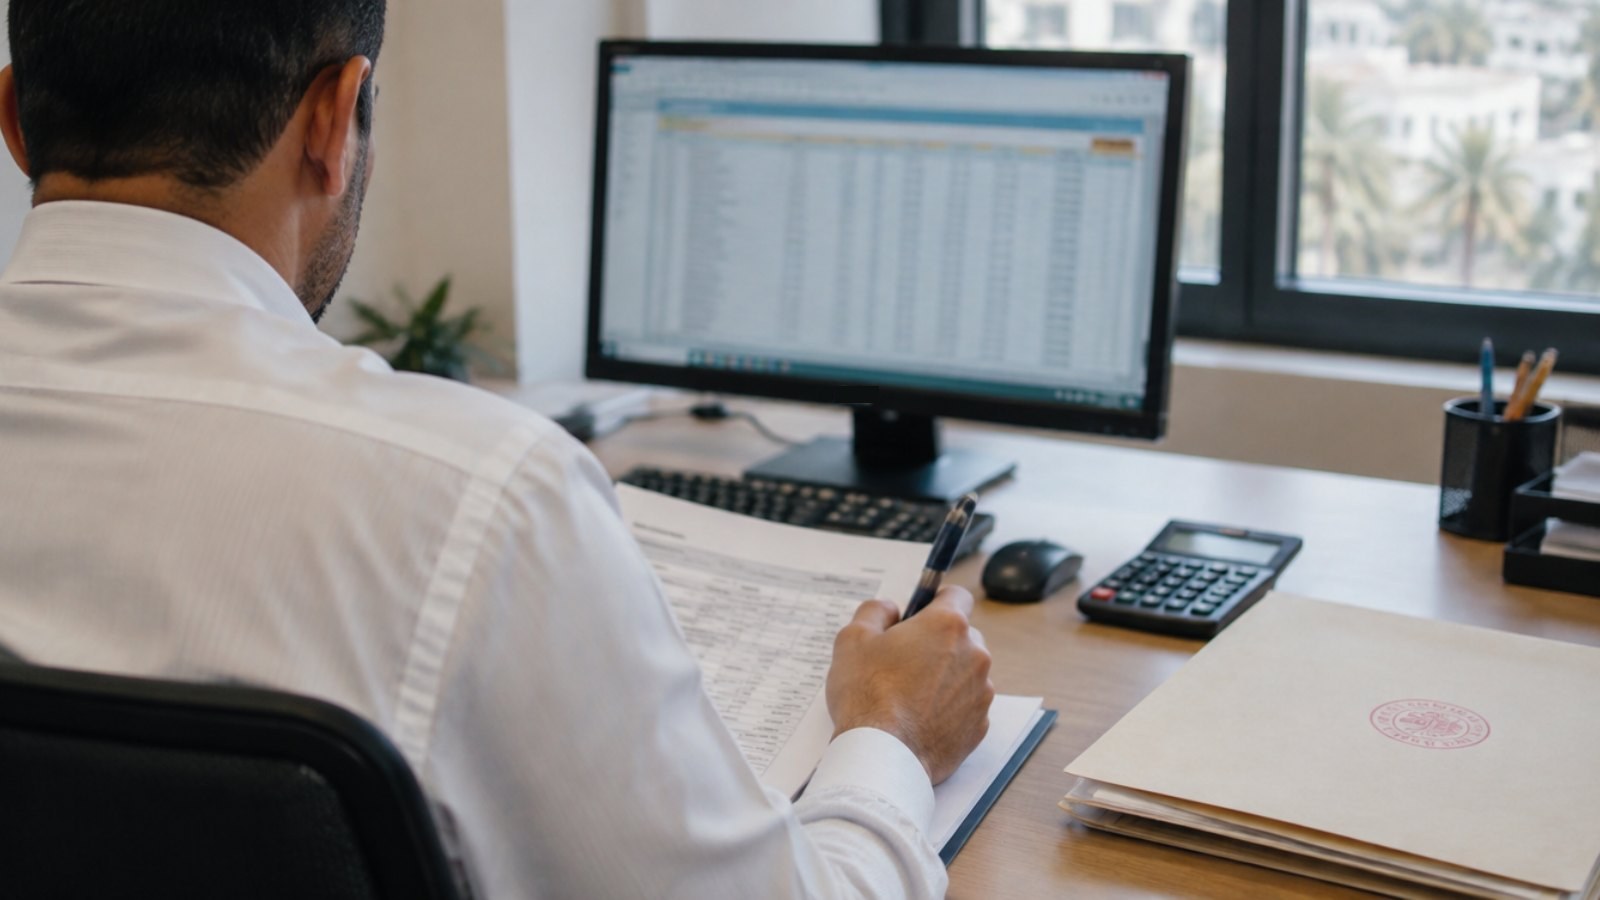
In a bank branch in Sfax, an adviser is putting together a mortgage file. At an insurer's head office in Tunis, a claims handler is drafting a rejection letter. In the compliance department, an analyst is summarising an audit report. All three have an AI assistant open in a browser tab, and all three handle data the law protects twice: as personal data and as professional secrecy.
For Tunisian banks and insurers, the question is no longer whether staff use generative AI. It is how to manage it in practice, without waiting for the next reform or the next incident.
AI is already part of Tunisian finance
The sector is openly interested. In May 2024, the Tunisian Federation of Insurance Companies devoted its Carthage insurance meetings to artificial intelligence, especially for claims handling and fraud detection. In September 2025, MAE Assurances announced an AI-based conversational agent, presented as a first for insurance in Tunisia.
Those projects are managed. The real risk comes from informal use: an employee pasting a bank statement, a loss adjuster's report or a customer list into a consumer tool to save time.
Three texts to keep in mind
A Tunisian financial institution that wants to manage AI has to combine three sources:
Organic Law No. 2004-63 on personal data, supervised by the INPDP: processing must be declared, data cannot be shared with third parties without a legal basis, and transfers abroad require authorisation. We covered it in our article on Law 2004-63 and offshore developers.
Law No. 2016-48 on banks and financial institutions. Article 61 binds directors and staff to professional secrecy. Article 81 governs outsourcing: a written agreement, prior notice to the Central Bank of Tunisia and compliance with Law 2004-63.
BCT Circular No. 2021-05 of 19 August 2021 on the governance of banks and financial institutions. It asks the board to protect the personal data of depositors and customers, and management to put matching protection mechanisms in place.
For insurers, the General Insurance Committee (CGA) acts as supervisor, and Law 2004-63 applies just as much to claims files and health data.
An AI tool is a service provider like any other
One point is often overlooked. When an online AI service processes customer data on behalf of a bank, it acts as an external provider. Under Law 2016-48, outsourcing requires a written contract and prior notice to the BCT. A subscription bought by a department on a company card meets none of these conditions. Then there is the transfer issue: most consumer AI assistants process data on servers outside Tunisia. Under Law 2004-63, such a transfer generally requires INPDP authorisation, which nobody requested when the tool crept in informally.
The BCT itself is stepping up its security: in July 2026 it launched a tender to build a security operations centre to monitor its digital environment around the clock. The signal to the market is clear.
The riskiest use cases
In banks and insurance companies, leaks tend to follow the same patterns:
a bank statement or repayment schedule pasted in to check a calculation;
a motor or health claim file summarised before a committee meeting;
a complaint letter translated from Arabic into French, with the customer's bank details;
a prospect file uploaded to prepare a sales campaign;
an anti-money laundering alert reworded, with the names of the people involved.
The last case is especially sensitive: a suspicious transaction report is confidential by nature, and disclosing it can create a far more serious problem than an ordinary data breach.
A five-step method
To move from a blanket ban to controlled use, an institution can:
map the AI tools in use, by business line and by branch;
approve one or two tools, with a contract that meets Article 81 and a review of data transfers under Law 2004-63;
define forbidden data: bank details, account numbers, national ID numbers, health data, anti-money laundering information;
check prompts and files on the workstation and anonymise what needs to be anonymised;
keep an incident log for internal audit, the risk committee and BCT inspections.
Format preserving anonymization keeps the tool useful: fictitious but valid bank details, one name swapped for another, the amount unchanged. Training still helps, but it is not enough, as we explain in why AI security training doesn't work.
Preparing for reform and European expectations
A draft organic law on personal data is being examined by Parliament. Among other things, it provides for rules on AI, impact assessments and a data protection officer. Tunisian banks linked to European groups already know these requirements, which are close to those in our EU AI Act and GDPR Article 32 checklist.
In summary
Tunisian banks and insurers already have a clear framework: Law 2004-63, banking Law 2016-48 and BCT Circular 2021-05. Applied to AI, it means treating every tool as a service provider, protecting professional secrecy and being able to prove what leaves the organisation. This is an operational project, not just a legal one.
ZeusLock detects bank details, account numbers, national ID numbers and health data in prompts and files, anonymises or blocks them on the workstation, and records every incident. Book a demo to see how it fits your institution.
Protect your data from AI leaks
See ZeusLock stop sensitive data before it reaches ChatGPT, Claude, Gemini and more, in a 30-minute demo.


